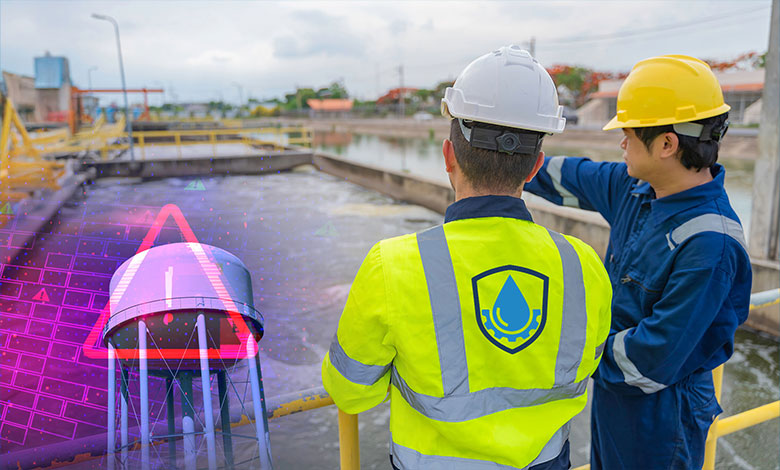
The first sign of trouble was not a warning on an IT dashboard. Water operators in several towns in Minnesota discovered that they could no longer reach the controllers that monitored and ran essential equipment. Passwords and IP addresses had been changed, leaving crews locked out. To keep water moving, utilities shifted to manual operations and sent experienced staff into the field.
Since July 27, water and wastewater utilities in at least seven states have reported incidents to the FBI, and some attacks degraded operations. Minnesota confirmed attacks on operational technology at more than 30 community water systems in late July. Other incidents followed, with reported effects including pressure loss, flooding, boil-water notices, and sustained manual operation. The FBI and EPA said attackers remotely accessed Internet-facing programmable logic controllers (PLCs)—the industrial computers that monitor or control physical equipment—and changed their configurations.
The Security Conversation Has a Blind Spot
These attacks did not begin with the servers, endpoints, firewalls, or cloud services that typically dominate municipal cybersecurity planning. They went after operational technology: the equipment and control systems that public works relies on to deliver essential services.
That is the organizational gap—between IT and OT. Readiness discussions often center on central IT while leaving out vendor and integrator access, legacy modems, shared credentials, and field controllers. Operational technology usually enters the security conversation only after a trigger, not as a routine part of it. By then, your team may be discovering critical dependencies during an incident instead of managing them beforehand.
Why the Gap Persists
IT may reasonably believe the operational technology is covered because endpoint protection, multifactor authentication, backups—all the traditional security tools—are in place. But the equipment under attack may belong to another department, rely on a third-party integrator, or predate modern security expectations. Some legacy devices cannot support the controls IT considers standard.
Ownership can also be fragmented. Public works buys and operates the equipment. A vendor installs it. An integrator enables remote access. IT carries the cybersecurity mandate but may never see the device on an inventory. This gap doesn’t form because of negligence; each group can fulfill its traditional role, while the connections between those roles remain unmanaged.
Shared Governance, Not an IT Takeover
The answer is not for IT to take control of pumps, valves, or other public works equipment. Better-run jurisdictions treat the boundary between IT and OT as a shared governance responsibility. IT, public works, engineers, leadership, vendors, and integrators agree on who owns each decision and how security requirements will be enforced.
One practice makes that model tangible: don’t purchase or connect a new operational device without a joint IT and public works security review. Before installation, the teams can document the asset owner, support contact, network connection, remote-access method, credentials, update process, and recovery plan. That review is faster and less expensive than reconstructing the same information during an emergency.
Shared governance also gives IT a legitimate place in vendor conversations without asking it to operate specialized equipment. Public works remains accountable for the process and machinery. IT helps set access, identity, connectivity, logging, and incident-response expectations. Both departments share the same objective: reliable public service.
Manual Operation Is a Capability—Not a Guarantee
Manual operation kept systems running during this summer’s incidents because experienced operators knew what to do. That success can hide another risk. Continuity is often assumed rather than tested, especially at smaller utilities where a few employees hold years of institutional knowledge.
What happens when those employees retire, are unavailable, or are supporting several sites at once? A manual fallback is only dependable if procedures are documented, current staff are trained, and the organization practices the handoff. Workforce development is therefore part of cyber resilience. Retaining skilled employees, attracting new ones, and deliberately sharing operational knowledge prevents the recovery plan from living in one person’s memory.
What to Do Monday Morning
Remote access is the common thread across these attacks, and there are some straightforward steps you can take right away to limit this access. Federal agencies recommend the following steps—and we encourage municipal and county IT leaders to start by working with public works to:
- Disable dormant accounts
- Require employees, vendors, and integrators to change passwords and use unique credentials
- Require multifactor authentication wherever it is supported
- Route necessary remote access through a secured gateway or VPN instead of connecting controllers directly to the Internet
These actions align with guidance from CISA, which urges utilities to remove publicly exposed PLCs and other operational technology from the Internet, validate external connections, and secure required remote access. It’s important to note that these are practical risk reductions, not a substitute for a broader review.
The One Thing to Do This Quarter
In the longer term, start by running a 30-day inventory and ownership review with public works. Identify each connected operational asset, who owns it, who supports it, who can reach it remotely, and how quickly that access can be revoked. Include vendor-installed cellular modems and other connections that may not appear in routine IT scans.
The goal is not a perfect inventory on day one. It is a shared view of the highest-impact assets and the riskiest access paths, with named owners for follow-up. That foundation makes future purchasing reviews, access changes, incident response, and continuity planning far more manageable.
A Fixable Gap
The divide between IT and OT in public works is real, but it is not permanent. Many of the most important first steps—bringing the right people together, documenting ownership, reviewing remote access, and testing continuity—cost little or nothing. A jurisdiction that starts now will be better prepared to protect operations without blurring departmental expertise.
Connection can help municipal and county IT teams on the IT side of that boundary, with security assessments, identity and access management, and security policy development, including remote and third-party access policies. Start with a joint inventory and ownership review, and then use what you learn to build a practical roadmap for closing the gaps.
Nicki Williams
Nicki Williams is Connection’s Vertical Alliance Manager for State and Local government. Nicki joined Connection in 2023 and is responsible for developing and implementing Connection’s overall strategy for State and Local governments. Nicki works with States and localities including Cities, Municipalities, special districts, nationwide to help develop and implement technology solutions to help with their digital transformation. Nicki has been in the technology industry for over 25 years. Nicki is part of a Public Sector advisory council with one of our distribution partners to help provide strategic guidance and industry insights within state and local government. Her expertise is invaluable in helping serve government end users and strengthening our ability to deliver full technology solutions that support vibrant communities across the country.